
Loading...
공급망 전반에 걸쳐 OEM에게 ISO/SAE 21434 표준에 부합하는 차량 사이버 보안을 입증하십시오. 차량 사이버 보안 엔지니어링 전반을 이해하는 심사원과 함께 ENX VCS 평가를 진행하십시오. DQS는 ENX에서 승인한 차량 사이버 보안 감사 제도(VCS) 제공 기관입니다. ISO/SAE 21434 표준에 부합하는 강력한 차량 사이버 보안 관리 시스템(V-CSMS)을 입증하고 ENX 플랫폼을 통해 자동차 공급망 전반에 걸쳐 결과를 공유하십시오.

Loading...
차량용 공유 사이버 보안 기준
차량 사이버 보안 감사 제도(ENX)는 자동차 산업에서 도로 차량 사이버 보안 엔지니어링에 대한 ISO/SAE 21434 표준에 따라 공급업체 감사를 표준화하기 위해 만들어졌습니다. ENX는 감사를 관리하고 결과를 교환하므로 단일 감사로 공급망 전반에 걸쳐 고객별 사이버 보안 감사가 파편적으로 이루어지던 방식을 대체할 수 있습니다. 이는 UN R155 및 지역 규정이 더욱 엄격해지는 상황에서 구조적인 이점입니다. ENX VCS 평가의 일반적인 효과는 다음과 같습니다. 평가의 가치는 적합성 입증을 넘어섭니다. 많은 조직에서 정기적인 감사 및 평가 프로세스를 지속적인 개선, 운영 투명성 및 부서 간 협업 강화의 틀로 활용합니다. 실제로 기업들은 다음과 같은 효과를 보고하는 경우가 많습니다.
ENX VCS 라벨을 요구하는 OEM과의 신규 비즈니스 자격을 유지하십시오. 고객별 사이버 보안 감사 및 설문 조사를 줄이십시오. ISO/SAE 21434에 부합하는 엔지니어링 및 ISO/PAS 5112 감사 적합성을 입증하십시오. UN R155에 기반한 OEM 규정 준수가 공급업체 감사로 이어지도록 지원하십시오. 공급업체 수준의 사이버 보안 성숙도를 강화하는 감사 기반을 구축하십시오.
지금 바로 DQS를 통해 ENX VCS 평가를 시작하세요
체계적인 평가 프로세스를 통해 시간과 내부 노력을 절약하세요. 지금 바로 ENX VCS 평가 견적을 요청하세요.

Loading...
ENX VCS 평가를 통해 누가 혜택을 받을 수 있을까요?
ENX VCS는 차량 사이버 보안 관련 제품 및 서비스를 설계, 통합 또는 공급하는 조직을 지원합니다. 지원 대상은 다음과 같습니다. E/E 부품, ECU 및 소프트웨어의 1차 및 2차 자동차 부품 공급업체, OEM 플랫폼에 통합하는 커넥티드 차량 서비스 및 텔레매틱스 제공업체, 사이버 보안 관련 개발 작업을 제공하는 엔지니어링 서비스 제공업체, 차량 내 또는 차량 관련 시스템에 기여하는 소프트웨어 및 AI 공급업체, 그리고 고객 및 당국에 V-CSMS 성숙도를 입증하고자 하는 OEM 및 1차 부품 공급업체입니다.
DQS는 ENX VCS 평가를 위한 신뢰할 수 있는 파트너입니다.
당사의 감사 접근 방식
ENX VCS 평가 프로세스는 명확하여 질문이 줄어들고 결과가 더 빨리 나옵니다. DQS에서 제공하는 ENX VCS 평가는 시작부터 끝까지 투명한 단계로 진행됩니다.
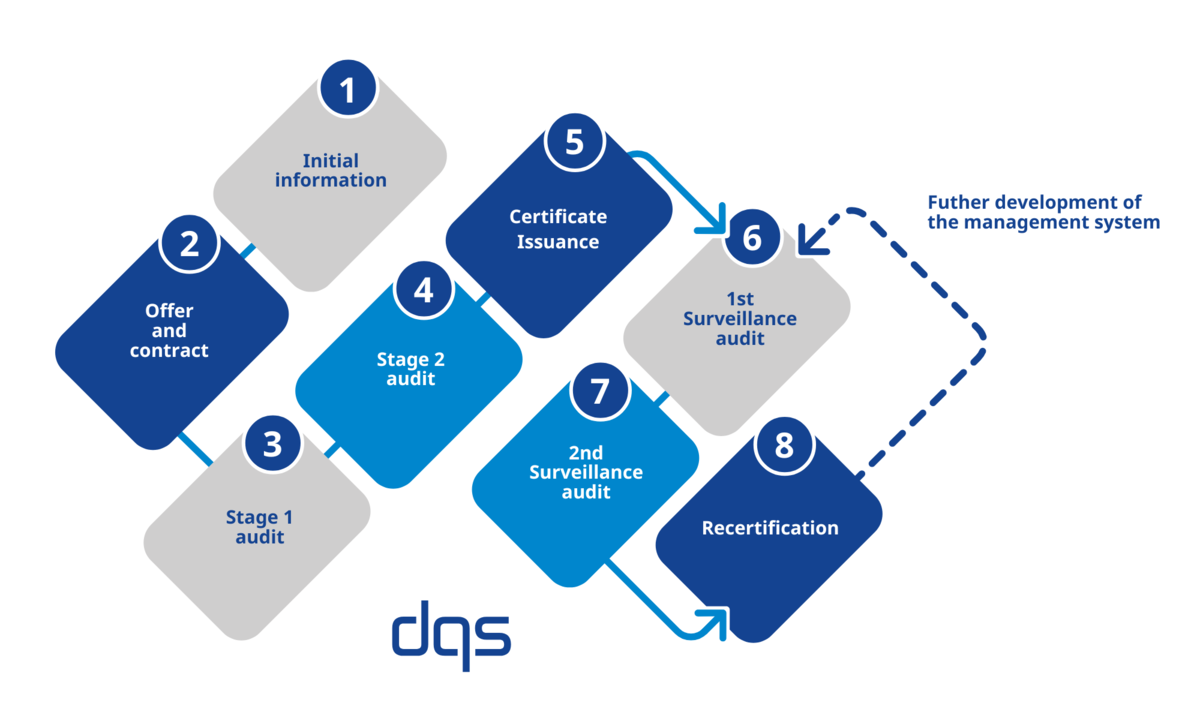
Once your ISO 9001 management system has been implemented across the organization, it is ready for certification. You will go through a multi-stage certification process at DQS. Your initial interaction will involve discussing your organization, your quality management system, and the objectives you aim to achieve with your ISO 9001 certification. Based on this, you will promptly receive a detailed quote tailored to your individual needs. For complex certification processes, project planning can help coordinate timelines and audit execution across sites or departments.
The certification audit begins with a system analysis (stage 1 audit) as well as an evaluation of your documentation, the results of your management review, and your internal audits. The goal is to determine whether your management system is adequately developed and ready for certification. In the next stage, the system audit (stage 2), your auditor evaluates the effectiveness of the management system processes on-site or through suitable remote techniques. After the audit is completed, you will receive a detailed presentation of the results in a closing meeting, along with information on potential areas of improvement for your company.
After the certification audit, the results are evaluated by the independent certification body of DQS. You will receive an audit report documenting the audit results. If all standard requirements are met, following a positive certification decision, you will receive the accredited ISO 9001 certificate of DQS.
To support continuous improvement and the ongoing effectiveness of your quality management system, key system components are audited at least once a year, during which potential areas for improvement are once again identified.
An ISO 9001 certificate is valid for three years. Well before expiration, a recertification is performed to confirm ongoing conformance with the ISO 9001 standard requirements. If all requirements of the standard are met, a new internationally recognized certificate will be issued.
Loading...
ENX VCS 평가 제안을 받기 위한 3단계 절차
1분 안에 요청을 보내실 수 있습니다. 제공해 주신 정보를 바탕으로 범위와 일정을 간략하게 확인해 드립니다. 감사 계획을 포함한 정확한 견적을 받아보실 수 있으며, 일반적으로 영업일 기준 이틀 이내에 다음 단계를 안내해 드립니다.
귀사는 ENX VCS 평가를 받을 준비가 되셨습니까?
V-CSMS가 ISO/SAE 21434 및 ISO/PAS 5112 요구사항에 맞춰 구현 및 조정되었습니다. 사이버 보안 거버넌스, 위험 관리 및 공급업체 감독 프로세스가 운영 중입니다. 개발 수명주기 전반에 걸쳐 사이버 보안 엔지니어링 활동이 문서화되었습니다. 사고 탐지, 대응 및 사후 운영 사이버 보안 프로세스가 정의되었습니다. ENX 시스템 등록이 완료되었고 내부적으로 감사 범위에 대한 합의가 이루어졌습니다. 귀사가 이러한 요구사항을 충족하면 DQS에 연락하여 ENX VCS 평가를 시작할 수 있습니다.
이미 인증된 경영 시스템을 보유하고 계십니까?
ENX VCS는 TISAX®, ISO/IEC 27001, ISO/IEC 21434 연계 심사, ISO 42001 및 IATF 16949와 효율적으로 결합될 수 있습니다. 이러한 통합 접근 방식은 여러 사이버 보안 및 품질 시스템 요구 사항을 관리하는 자동차 부품 공급업체의 심사 중복을 줄여줍니다.
ENX VCS 평가 관련 자주 묻는 질문
Most organizations complete the ISO 9001 certification process within three to six months after their quality management system is fully implemented. The actual timeline depends on company size, the number of sites, scope complexity, and your audit-readiness. DQS plans a realistic schedule with you from initial inquiry to certificate issuance. Learn more about ISO 9001.
An ISO 9001 certificate issued by DQS is valid for three years. Continued validity depends on successful surveillance audits, which take place at least once a year and confirm that your quality management system remains effective. A recertification audit before the three-year mark renews the certificate for the next cycle. Learn more on our ISO 9001 Knowledge Center page.
The cost of ISO 9001 certification depends on your organization’s size, the scope of the management system, the number of sites included, and any industry-specific factors. Audit days follow accreditation rules and are calculated against standardized formulas, so quotes from accredited certification bodies are transparent and directly comparable. Request a personal quote to receive a tailored estimate for your specific scope.
Once your ISO 9001 management system is implemented, the external certification audit itself usually requires only a few days of on-site or remote audit time per site, plus internal preparation. The biggest driver of effort is the maturity of your processes and documentation — not the audit itself. DQS keeps your team’s involvement focused on what adds value through clear scope, efficient planning, and a modernized audit journey.