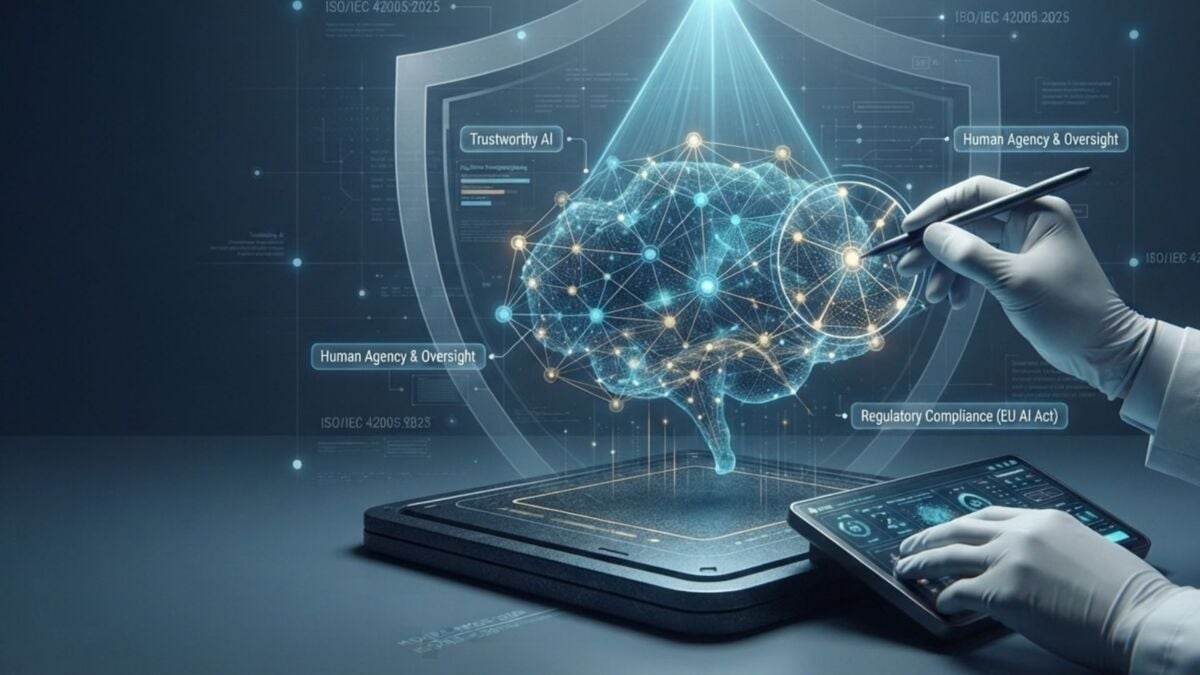
For enterprises and organizations deploying artificial intelligence architectures or implementing automated algorithmic systems, managing socio-technical risk is a critical governance priority. Entities leveraging AI bear the organizational responsibility of ensuring their systems remain trustworthy, transparent, unbiased, and safe to effectively mitigate operational, legal, and ethical liabilities throughout the system lifecycle.
The AI Impact Assessment (AI-IA) serves as the definitive tool to manage, evaluate, and control these complex risk vectors.
- Verifiable AI trustworthiness and algorithmic transparency,
- Ethical governance and safety embedded into organizational architecture,
- Rigorous execution of an AI risk management process, and
- Continuous optimization of regulatory compliance and performance thresholds.
What is an AI Impact Assessment (AI-IA)?
The AI Impact Assessment (AI-IA) is a proactive compliance and governance framework designed for organizations to execute prior to the commercialization, deployment, or procurement of AI applications, foundation models, or algorithmic workflows. This assessment systematically evaluates whether an AI system poses risks to fundamental rights, health, safety, or societal well-being.
Technically, an AI-IA is a structured process of identifying, analyzing, and treating potential lifecycle impacts in strict accordance with the ISO/IEC 42005:2025 standard, which may be extended to address the associated requirements in regulatory mandates, such as Fundamental Rights Impact (FRIA) Assessments required by EU AI Act. By mapping data lineage, evaluating systemic biases, and establishing risk mitigation strategies during the design phase, organizations can implement automated technologies while optimizing cost-effectiveness and compliance integrity.
Who is AI-IA suitable for?
AI-IA is essential for all organizational stakeholders across the AI lifecycle, particularly those subject to AI-relveant regulations, such as EU AI Act, or aligning with international frameworks:
- Providers and Deployers of High-Risk AI Systems (e.g., critical infrastructure, biometrics, employment algorithmic scoring, credit evaluation).
- Developers of General Purpose AI (GPAI) and large-scale language or foundation models.
- Public and Private Entities utilizing automated decision-making systems (ADMS) that materially impact consumer access, health platforms, or legal rights.
What are the benefits of AI-IA?
- Upfront Risk Mitigation: Identifies algorithmic flaws, drift liabilities, and compliance gaps prior to capital-intensive deployments.
- Regulatory Alignment: Demonstrates definitive compliance with relevant regulations, such as EU AI Act and supports an ISO/IEC 42001 (AIMS) management structure.
- Enhanced Institutional Trust: Establishes transparency and accountability, assuring B2B clients, regulators, and the public that data practices and model outputs are ethically governed.
- Explainability Verification: Bridges internal communication gaps by deconstructing "black box" processing to identify model constraints and edge-case operational boundaries.
Functions of AI-IA Reporting
An AI-IA report fulfills two primary structural operations
- System Inventory: Informs key internal and external stakeholders of the AI system's architectural capabilities, data processing boundaries, and inherent or mitigated risks across its lifecycle.
- Actionable Tracking: Functions as a technical remediation mechanism to track and log software corrections, data filtering, retrain parameters, and human-in-the-loop (HITL) control mechanisms.
When is an AI-IA required?
Organizations should initiate or update an AI-IA under the following conditions
- Prior to provisioning or procuring new AI models, services, or algorithmic logic.
- When an AI system falls under the High-Risk classification or transparency tier mandates of regional regulations like the EU AI Act.
- Upon significant system modifications, changes to underlying training data sets, or the detection of substantial model drift and performance degradation.
- Following updates to national, international, or industry-specific AI compliance legislation.
Contents of an AI-IA Report
Depending on the risk tier and system complexity, an AI-IA report provides comprehensive documentation, typically addressing:
- The technical scope, architecture, and operational boundaries of the AI system.
- Risk classification profiles under relevant global legal standards.
- Data governance evaluations, including data quality, lineage, and bias assessments.
- Socio-technical risk assessments focused on human safety and fundamental rights.
- The technical risk treatment plan detailing accuracy metrics, human oversight protocols, and cybersecurity robust guardrails.
- An executive public summary to satisfy transparency requirements for end-users.
For a particular assessment, the contents of the report may be adjusted.
How does AI-IA work?
Architecture and Operational Boundary Analysis
We evaluate the structural parameters, data lineage, business objectives, and intended use-cases underpinning your AI system.
Core AI Trustworthy Principles Auditing
The system architecture is rigorously audited against the foundational pillars established by ISO/IEC 42005:2025 and current regulatory benchmarks:
- Human Agency and Oversight: Validating intervention protocols and human-in-the-loop (HITL) architecture.
- Technical Robustness and Safety: Assessing resilience against adversarial vulnerabilities and structural system errors.
- Privacy and Data Governance: Verifying data source legitimacy, privacy preservation mechanisms, and data minimization.
- Transparency and Explainability: Reviewing decision traceability and the clarity of user-facing disclosures.
- Diversity, Non-discrimination, and Fairness: Conducting algorithmic bias audits to uncover and mitigate systemic or hidden data discrimination.
- Societal and Environmental Well-being: Analyzing broader socio-economic impacts and computational energy efficiency footprints.
Risk Classifications for Technical Guardrails
This phase focuses on the classifications of risks, which will be used as input by the client for corrective actions, technical boundaries, and organizational policies to neutralize the identified risks.
AI-IA Reporting
We will deliver an audit-ready, authoritative AI-IA report featuring verified findings, technical compliance mappings, and final executive determinations.
Financial and Engagement Terms
Because AI system architectures, deployment environments, and training datasets vary widely, assessment costs cannot be calculated as a fixed rate. DQS HK provides assessment proposals based on an objective technical evaluation of your specific system complexity and regulatory target markets. Please contact us for an assessment blueprint.
To assist you in refining this copy for your corporate site or establishing the technical scope for an assessment, please clarify:
- What is the primary function or commercial use case of the AI system being evaluated?
- Is the system developed natively in-house or procured as a third-party application / API?
- Which jurisdiction or regulatory framework (e.g., the EU AI Act, specific regional standards) is your immediate priority for compliance?
Why Choose DQS?
- Over 35 years of global leadership in international management systems certification, including specialized frameworks for information security (ISO/IEC 27001) and Artificial Intelligence Management Systems (ISO/IEC 42001).
- A network of highly credentialed technical assessors holding advanced qualifications in data science, ethical AI governance, and IT systems auditing.
- Pragmatic, value-driven feedback that effectively bridges the gap between complex software engineering requirements and enterprise compliance mandates.